Blockchain and smart contracts built for shared, tamper-evident records
The test before any blockchain work is simple. If one organisation controls every writer, a database with an append-only audit log gives tamper evidence far more cheaply. A ledger earns its place when several parties write to the same record and none will let another hold the master copy. Then we choose the network for those parties, Hyperledger Fabric for known companies wanting permissioned access and no public exposure, an EVM chain when anyone must be able to verify the record. Only what must be shared goes on chain, usually hashes, ownership and state transitions, while documents stay in your systems or on IPFS and personal data never leaves your database, each anchored by its fingerprint. Smart contracts are kept small and written with an upgrade path, because a bug on an immutable ledger cannot be patched quietly.
Digital twins built from live sensor data and validated against history
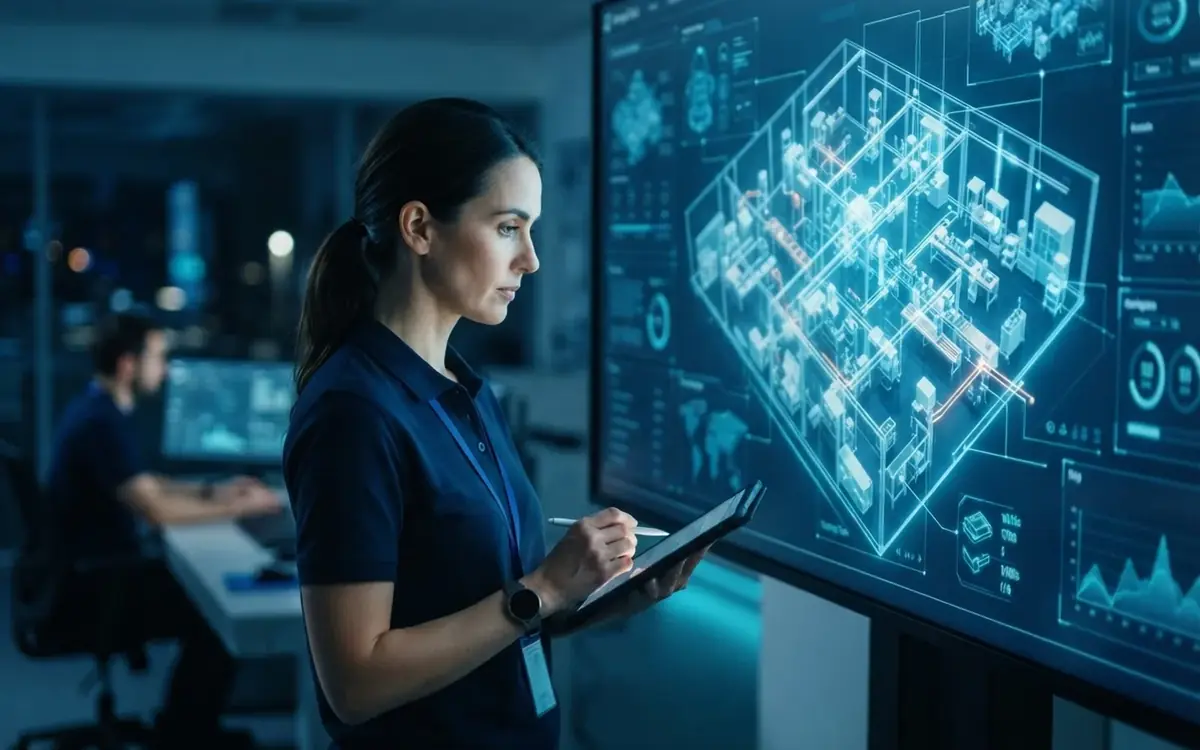
A twin is only as useful as it is faithful to the asset, so we build it in stages that each narrow the gap. The first stage is descriptive, with telemetry from PLCs, SCADA historians and IoT gateways streamed into a model of the asset and its topology, so state and history sit in one place. The second is predictive, where models trained on that history forecast failures or throughput, and the third is prescriptive, where you change a parameter in the twin and see the consequence before touching the plant. The step most projects skip is validation. Before anyone trusts a what-if result we replay past periods through the twin and compare its output with what actually happened, and we state the error band. We start with one line, one fleet or one building, never the whole estate.
Applied cryptography with key management you can show an auditor
Cryptography fails in production through mishandled keys far more often than through broken algorithms, so key management gets more design time than cipher choice. We use well-studied primitives, AES-GCM for data at rest, TLS 1.3 in transit, ECDSA or Ed25519 for signatures and SHA-256 for hashing and anchoring. Keys live in a cloud KMS or hardware security module, never in code or configuration, with rotation schedules, separation of duties for the people who can approve their use, and a documented ceremony for generating the roots. Every signing and decryption operation is logged, and tamper-evident records are built as hash chains so a single altered row breaks every later one. The threat model is written down before launch, and afterwards certificate expiry, key age and failed verifications are monitored so trouble shows as an alert rather than an incident.