Behavioural threat detection built on your own telemetry
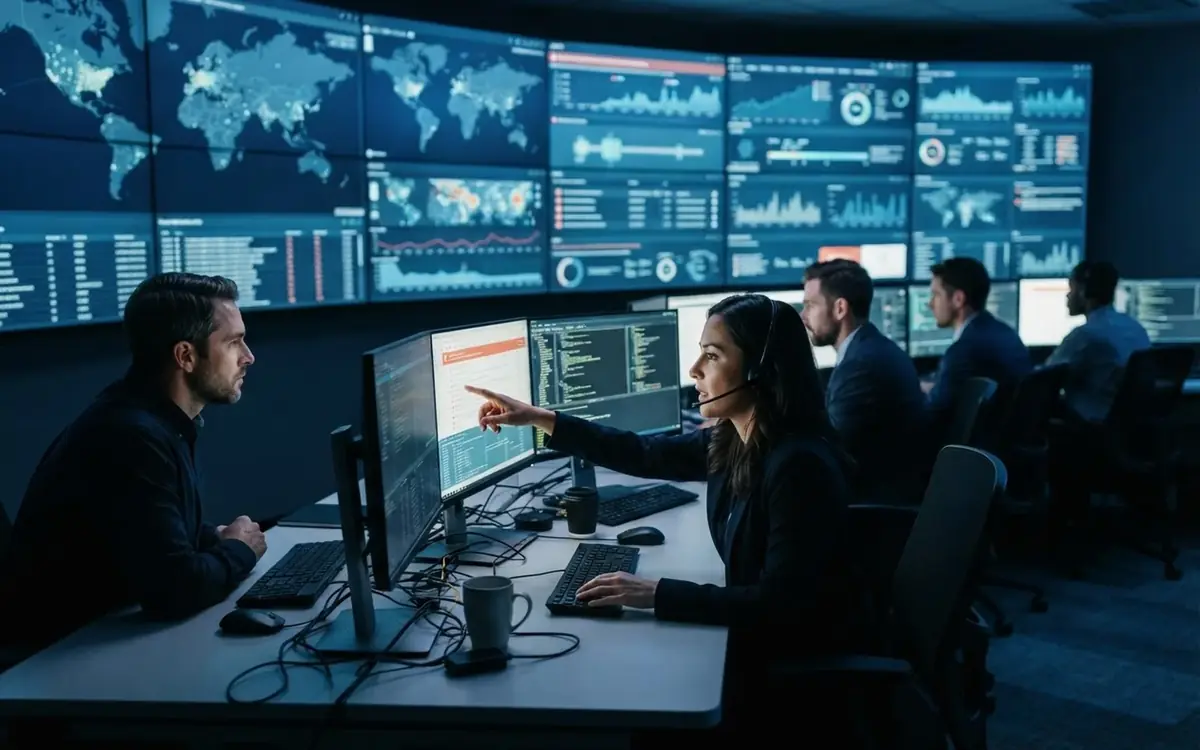
Behavioural detection is only as good as the telemetry beneath it. Endpoint process and file events from your EDR, sign-in and privilege changes from the identity provider, flow records from the network and audit logs from AWS or Azure are normalised into a SIEM such as Elastic or Wazuh, with a common schema so one query follows a user from laptop to cloud console. On top of that the models build a baseline per user, host and peer group, which hours, which systems, how much data, which parent process launches which child. An alert fires on the distance from that baseline, not on a string match, which is how novel malware or a quietly compromised account surfaces. Each alert arrives with the entity, the deviation and the supporting events attached, so an analyst starts with evidence rather than a search.
Automated incident response playbooks tiered by confidence and blast radius
The question is not whether to automate response but which actions may run without a human, and the answer depends on how reversible each one is. Isolating a laptop from the network is cheap to undo and buys time, so it runs on a high-confidence detection within seconds. Disabling a service account on a production system can stop a business process, so that playbook enriches the alert, proposes the action and waits for a single approval in the ticket or chat channel your team already uses. We write playbooks in tiers along that line, test them in a staging copy of your SIEM and EDR before they touch production, and rehearse them with your team in a tabletop exercise. Every automated action can be reversed with one command, which is what makes the fast tier safe to run unattended.
Continuous compliance evidence mapped to the frameworks you report against
Auditors ask for evidence that a control existed and worked on a given day, and a monitored environment produces exactly that as it runs. We map each detection, access rule and response playbook to the controls it satisfies in the frameworks you report against, whether ISO 27001, SOC 2, PCI DSS or the NCA Essential Cybersecurity Controls in Saudi Arabia, and the SIEM collects the proof automatically, log retention, alert handling times, access reviews, configuration drift. The same pipeline gives leadership the numbers that matter, mean time to detect, mean time to contain, false positive rate and coverage of assets, tracked month on month so that tuning is visible. The baselines are retrained as your estate changes, and your team is left with runbooks, dashboards and a detection catalogue they can extend without rebuilding anything.